
I would recommend ThreatLocker without reservation to anyone who wants to drastically reduce their attack surface and minimize risk. It's very easy to use, and it's a very powerful tool. It should be in every IT professional's tool belt.
My overall experience with ThreatLocker has been phenomenal. I was blown away by the support. If we have an issue, we send an email, and within three to five minutes we're on the phone with someone. That level of responsiveness has made rolling out ThreatLocker simple, easy for our end users, and ultimately successful.
Controls like ThreatLocker make attacks more difficult and provide the visibility needed to detect and stop unauthorized activity.
It’s important for us to partner with leading-edge companies like ThreatLocker to achieve the most resilient cybersecurity posture possible.

ThreatLocker solved alert fatigue for us. What I noticed was that the product, the interface, and the amount of data it surfaces allowed some of my more junior team members to become effective responders within our environment. It became a force multiplier for my team.
ThreatLocker provides that extra key to block anomalies that nothing else can do. It gives me a great deal of comfort as an IT director.
ThreatLocker gave us the granular control we were looking for and provided real peace of mind.
ThreatLocker significantly reduced alert fatigue for our team. Before ThreatLocker, we spent countless hours reviewing EDR alerts and investigating potential threats. It wasn't efficient and consumed a lot of our time. With [the] ThreatLocker['s] prevention-first approach, threats are blocked before they can execute, giving us greater peace of mind and allowing our team to focus on more strategic work.


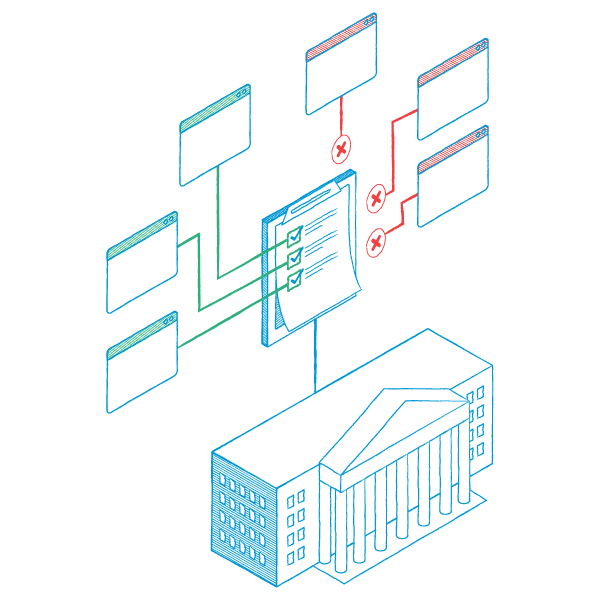
Every new technology initiative introduces new pathways for attackers.
Something as unassuming as a single unauthorized application can disrupt operations and force your team to shift focus from mission execution to incident response.
You can avoid these scenarios with proactive controls from ThreatLocker.
