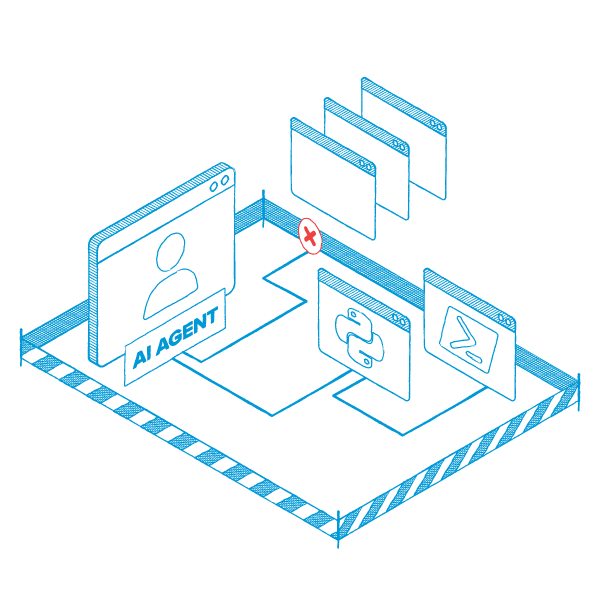
Ditch the added complexity for lean IT teams and disruption for students, faculty, and researchers that is often associated with applying Zero Trust controls across decentralized, user-heavy environments. Get a practical framework that enables both hardened security and straightforward access.

ThreatLocker MDR alerted me in real time multiple times. One night around 11 p.m., I received an alert that a user had been moved into a remote users group. It turned out to be one of my staff members working late—but moments like that make it feel like ThreatLocker MDR truly has my back.
Since implementing ThreatLocker, we estimate it has saved about 20% of our engineers’ annual time previously spent handling security-related situations. With ThreatLocker, containment and validation happen much more efficiently, and the platform operates reliably once deployed.
We're just one phishing link or one malicious file away from an incident every day. What ThreatLocker does is provide that bottom layer in our layered security approach. Even if all the other systems we have fail and something malicious gets onto our network, ThreatLocker will stop it from running.
We sleep better. Our security posture is much stronger, and day-to-day operations are calmer. Software requests are easier because their Managed Detection and Response (MDR) and Cyber Hero Team handle approvals for applications we already use, while we keep control over anything new. That reduces workload without compromising security.

We were supported throughout the entire process. Years later, we still have regular meetings with our ThreatLocker team. Our expectations were greatly exceeded. ThreatLocker has been one of the best installations we've done. It really was what they said it was going to be.
When we needed cybersecurity insurance, we ran into challenges because we didn’t have a 24/7 SOC. The MDR solution gives us 24/7/365 monitoring, which helped us meet those requirements.
Teachers reacted very positively to the rollout. They found it reassuring to know expert eyes were on the system and that we were protecting their computers in a proactive rather than reactive way. ThreatLocker has allowed me to reprioritize my time and not constantly worry about end-user computers.
ThreatLocker helps us meet compliance requirements related to personal data protection by giving us oversight and authorization control over third-party access to university systems.
Our onboarding experience with ThreatLocker was seamless. We had a great solutions engineer who walked us through the product, helped us configure our servers, and assisted with rolling it out to our individual workstations. Overall, it was not a very difficult process.
ThreatLocker integrated wonderfully with our existing security stack. It complemented the Microsoft Defender EDR solution we already had and ultimately exceeded our expectations for what it could provide.

Avoid added complexity for your IT team while reducing ransomware risk, controlling identity-based threats, and securing your entire academic environment. Strengthen your cybersecurity posture while supporting compliance, audits, and cyber insurance requirements.
